Android Security Architecture and Modern App Isolation Explained
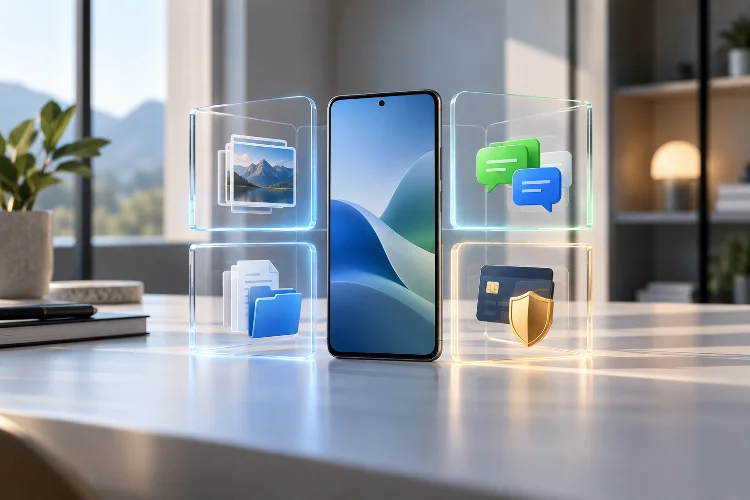
Your Android phone may contain banking apps, private messages, work documents, photos, passwords, and dozens of applications from completely different developers.
Yet under normal conditions, a random game cannot simply open your banking app’s private files or read another application’s passwords.
That separation is not an accident.
Android security architecture is built around multiple layers of isolation that limit what applications can see and do. Every app operates inside a restricted environment, while permissions control access to sensitive resources such as the camera, microphone, contacts, and location.
Modern Android adds additional defenses through SELinux, syscall filtering, secure interprocess communication, hardware-backed cryptography, and verified system software.
The important idea is defense in depth. Android does not rely on one security feature to protect everything. Instead, several protections overlap, so bypassing one barrier does not automatically provide complete access to the device.
Understanding these layers makes Android security much easier to appreciate – and explains why application isolation remains one of the platform’s most important defenses.
Every Android App Starts Inside a Sandbox
The foundation of Android application security is the Application Sandbox.
When an app is installed, Android normally assigns it a unique Linux user ID, or UID, and runs it within its own process. The Linux kernel then uses that identity to separate the application’s resources from other apps.
Think of every application as renting its own locked apartment.
Instagram can use its own private files. A banking application has another private area. A game gets a separate environment. One tenant cannot simply walk into another apartment because the operating system enforces the boundaries.
By default, applications have limited access to the operating system and cannot directly interact with another app’s private resources. Android’s sandbox also applies to native code, meaning developers do not escape the security model simply because part of an application is written in C or C++.
This kernel-level isolation is important because it places enforcement below the Android application framework itself.
Even if an application behaves badly, its default privileges remain limited.
Unique UIDs Keep Private App Data Separate
Android’s use of unique UIDs is one of the reasons app data can remain isolated even when hundreds of applications share the same phone.
Linux traditionally separates users by assigning them different identities and file permissions. Android repurposes that model so applications effectively behave like individual Linux users.
An app therefore normally cannot read another application’s private directory simply because it knows where the files are stored.
App signing also contributes to this identity model.
Android requires applications to be signed, and the Package Manager checks that signature when the APK is installed. Signing helps establish application identity and controls situations where apps are allowed to share special trust relationships.
For normal third-party applications, separate UIDs and separate sandboxes are preferable.
Android’s security guidance specifically recommends minimizing shared system identities and keeping processes isolated whenever possible.
That reduces the damage one compromised component can potentially cause.
SELinux Adds Another Security Wall
Linux file permissions are powerful, but Android does not rely on them alone.
The platform also uses Security-Enhanced Linux, usually called SELinux, to enforce mandatory access control.
SELinux applies security policies to processes across the system, including processes running with elevated Linux privileges. Android’s documentation notes that SELinux can enforce mandatory access control even over root or superuser processes.
This provides another defensive layer beyond basic UID permissions.
Android progressively strengthened SELinux isolation over multiple releases. Since Android 9, nonprivileged apps targeting the required API level have operated inside individual SELinux sandboxes, adding mandatory access controls to per-app separation.
This matters because security problems rarely follow neat rules.
If an attacker somehow reaches a more privileged component, SELinux policies can still restrict which resources and services that component is allowed to access.
It is a little like getting through a building’s front door but discovering that every important room still has its own security lock.
Permissions Provide Controlled Access Outside the Sandbox
A completely isolated application would not be very useful.
Navigation apps need location. Camera apps need the camera. Voice-recording apps need the microphone, while communication software may need contacts or notification access.
Android therefore uses permissions to provide controlled exceptions to the sandbox.
Applications declare the capabilities they require, while sensitive permissions can require explicit user approval. Android’s privacy documentation explains that apps operate within limited-access sandboxes and must request permissions when they need protected resources outside those boundaries.
Modern Android also gives users increasingly granular control.
Location permissions, for example, can distinguish between approximate and precise location. Access may also be limited to periods when the application is actively being used.
This follows the principle of least privilege: an application should receive only the access it actually needs.
That approach reduces risk if the application later contains a vulnerability or is otherwise compromised.
Giving a flashlight app unrestricted access to contacts, location, microphone, and files would create unnecessary exposure. Modern permission controls make that harder to justify and easier for users to notice.
Apps Communicate Through Controlled Interfaces
Applications sometimes genuinely need to communicate with each other or with Android system services.
Android does not solve this by removing sandbox boundaries.
Instead, communication generally happens through controlled interprocess communication mechanisms such as Binder.
This allows one process to request a service from another without gaining unrestricted access to the other process’s memory or private files.
App signing and permissions can also restrict who is allowed to access particular exported components.
Android specifically notes that signature-level permissions can limit certain functionality to applications signed with the same developer key while the apps continue to maintain distinct UIDs and sandboxes.
This architecture is safer than letting apps directly inspect one another.
Imagine a banking application that wants to use Android’s biometric authentication service. It does not need unrestricted access to the system process implementing biometrics. It only needs a carefully defined interface for requesting authentication.
Well-designed IPC keeps that relationship narrow and controlable.
Syscall Filtering Strengthens the App-to-Kernel Boundary
The Linux kernel exposes system calls, or syscalls, that programs use when requesting low-level operating-system functionality.
Because the kernel is such a valuable target, reducing unnecessary access to these interfaces can make attacks more difficult.
Android strengthened its application sandbox by introducing seccomp-bpf filtering for apps beginning with Android 8.0. These filters restrict which system calls application processes are allowed to use.
This follows another useful security principle: reduce the available attack surface.
If normal applications never need certain low-level kernel operations, allowing them access creates risk without providing much benefit.
A syscall filter therefore works somewhat like a security desk with a list of approved requests.
Even though an application can communicate with the kernel, it does not automatically receive access to every possible kernel interface.
Combined with UID separation and SELinux, this creates several layers between ordinary application code and highly privileged system functionality.
Hardware-Backed Keystore Protects Sensitive Keys
Software isolation is only part of modern Android security.
For especially sensitive cryptographic operations, Android can use hardware-backed security.
The Android Keystore system can store cryptographic keys so their sensitive key material is handled inside protected hardware environments rather than normal application memory.
Android’s KeyMint architecture commonly performs secure cryptographic operations inside a Trusted Execution Environment, or TEE.
Applications still access their keys through normal Android APIs.
However, one app generally cannot simply request another application’s keys. Android’s Keystore design incorporates the caller’s UID into access control, helping keep key material separated between applications.
This can protect credentials used for encrypted storage, authentication, digital signatures, and other sensitive operations.
Android also supports authentication-bound keys.
For example, a cryptographic key can be configured so an operation succeeds only after the user authenticates using an approved credential. Components such as Gatekeeper and secure biometric systems can participate in that process.
The result is stronger seperation between normal application execution and highly sensitive secrets.
Verified Boot Protects the Platform Beneath Apps
Application isolation becomes much less useful if the operating system beneath the apps has already been modified by an attacker.
Android therefore also protects the boot process.
Verified Boot creates a chain of trust beginning from a hardware-protected root and continuing through the bootloader and verified system partitions. Its goal is to ensure that executed system code comes from a trusted source rather than unauthorized modification or corruption.
This complements application sandboxing.
The sandbox protects apps from one another, while Verified Boot helps establish confidence in the platform responsible for enforcing those boundaries.
Android also uses Trusted Execution Environments such as Trusty on supported hardware. Trusty runs separately from the normal Android environment and provides a more strongly isolated location for security-sensitive services.
Again, the pattern is defense in depth.
A secure Android phone is not protected by one magical sandbox. It combines kernel security, hardware trust, application isolation, cryptography, and policy enforcement.
Why Modern App Isolation Still Cannot Guarantee Perfect Security
No security architecture makes software invulnerable.
Android itself acknowledges that individual sandbox protections are not impossible to bypass. A sufficiently serious kernel or privileged-system vulnerability could potentially allow an attacker to cross security boundaries.
This is why overlapping defenses matter.
An exploit may need to bypass app isolation, overcome SELinux policy, obtain higher privileges, defeat additional kernel protections, and access protected data – all without being stopped by another layer.
Regular security updates are therefore extremely important.
Application developers also play a role. An app can weaken its own protection by exporting components carelessly, storing sensitive information insecurely, requesting unnecessary permissions, or creating unsafe communication interfaces.
Strong operating-system isolation helps enormously, but good application design remains essential.
Security is most effective when the platform, manufacturer, developer, and user all avoid creating avoidable vulnerabilites.
Android security architecture is built around the idea that applications should not automatically trust or access one another.
Unique Linux UIDs and the Application Sandbox create the basic isolation boundary.
SELinux adds mandatory access controls, syscall filtering reduces kernel exposure, permissions provide controlled access to sensitive resources, and IPC lets apps communicate through defined interfaces instead of bypassing isolation.
Hardware-backed Keystore, Trusted Execution Environments, and Verified Boot extend that security below ordinary application software.
The result is a layered model rather than a single protective feature.
When evaluating Android security, look beyond antivirus claims or privacy labels. Long-term security updates, strong hardware-backed protection, responsible permissions, and well-designed application isolation matter far more.
Understanding those layers makes it easier to see why modern Android devices can safely run hundreds of unrelated apps on the same hardware.